Insights ·
The AI SOC Reality: What Seat Four Taught Me About Trust, Speed, and Control
From the 2023 HCRA State Championship to the rise of autonomous AI in cybersecurity.
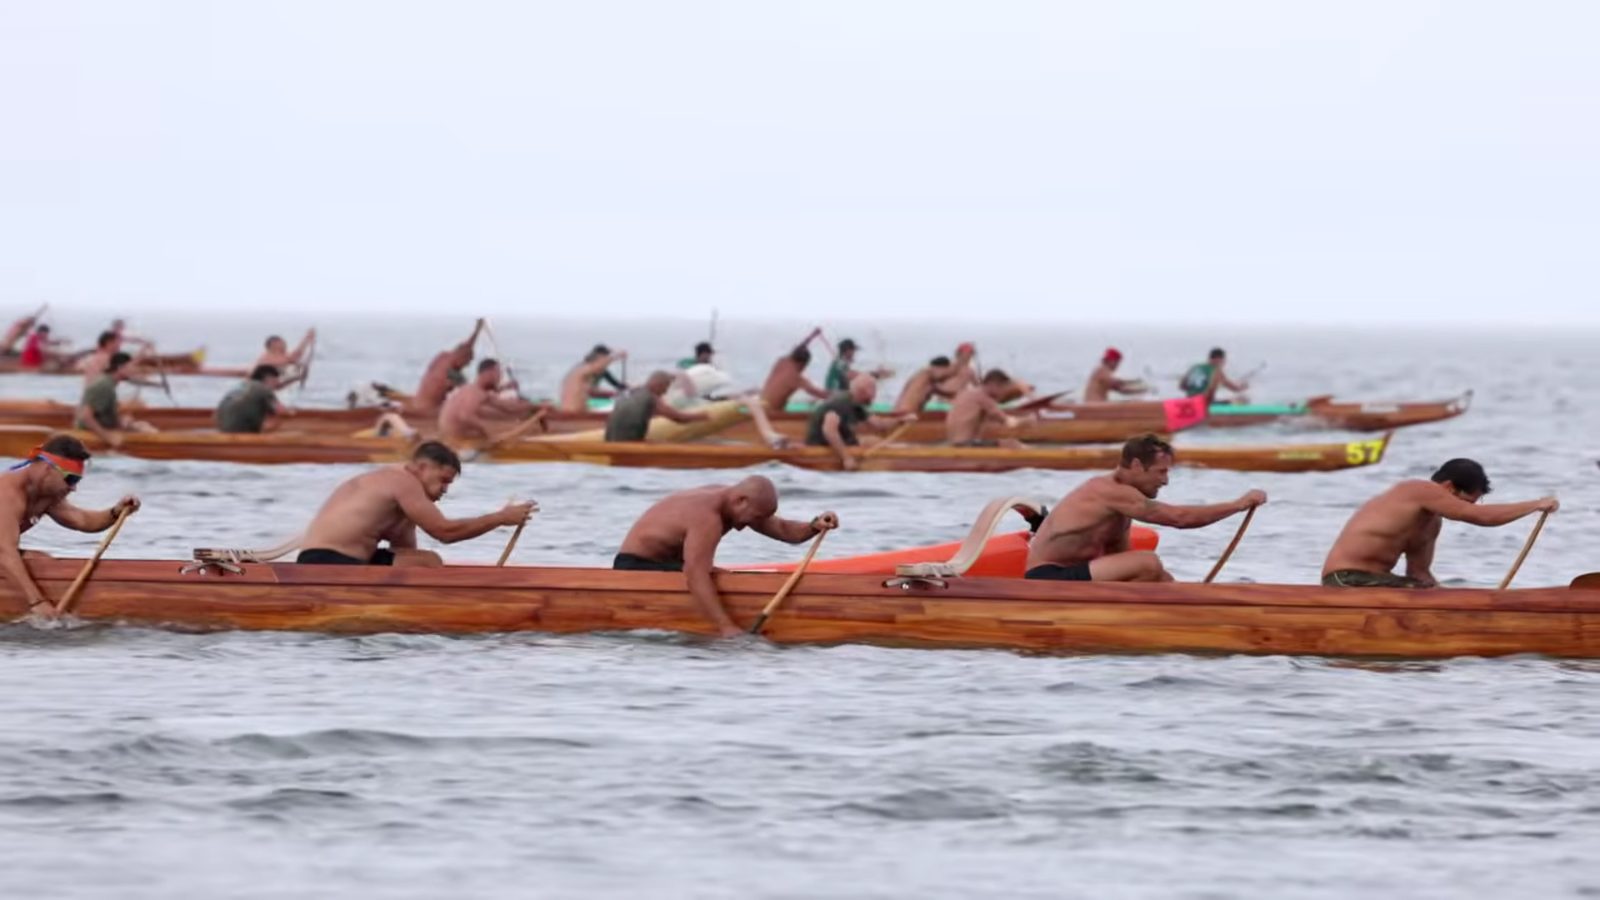
In this photograph from the 2023 HCRA State Championship in Hawaii, I'm sitting in the fourth seat of our outrigger canoe.
For those familiar with outrigger racing, every seat has a purpose. The first seat establishes the stroke, the crew generates momentum, and the steersperson keeps the canoe on course.
My responsibility in the fourth seat was to contribute power, maintain rhythm, and remain synchronized with the crew.
I couldn't see everything happening around me, nor did I need to. I trusted the paddlers ahead of me, those behind me, and the person steering our canoe.
Every stroke mattered. But no individual paddler, regardless of strength or experience, could achieve the same result alone.
Looking at this photograph today, I see a compelling parallel with something I've spent much of my professional career working on: technology, cybersecurity, and increasingly, artificial intelligence.
Specifically, the emergence of the AI-powered Security Operations Center (SOC).
The Faster We Paddle, the More Coordination Matters
Cybersecurity teams have spent years managing growing volumes of security alerts, sophisticated threats, and increasingly complex technology environments.
Now, Agentic AI promises to fundamentally change security operations.
Instead of relying exclusively on human analysts, organizations can deploy specialized AI agents capable of detecting suspicious activity, investigating threats, correlating evidence, and recommending or executing remediation.
Imagine a security operation powered by multiple agents:
- Detection Agent: Identifies suspicious activity across endpoints, networks, identities, and cloud environments.
- Investigation Agent: Correlates events, gathers evidence, and determines potential threats.
- Validation Agent: Independently challenges findings before critical decisions are made.
- Response Agent: Recommends or executes remediation within established authorization boundaries.
Each agent has a responsibility, much like each paddler in an outrigger canoe.
But what happens when one agent acts outside its assigned role? Or makes a decision based on incorrect information provided by another?
In canoe racing, losing synchronization can disrupt the entire crew.
In cybersecurity, the consequences can be considerably greater.
Intelligence Doesn't Automatically Mean Good Judgment
One lesson I've learned from paddling is that working harder isn't always the answer.
Power must be delivered at the right moment, in the right direction, and in coordination with everyone else.
AI security agents face a similar challenge.
Imagine an AI agent detecting unusual administrative activity in a production environment. Within seconds, it identifies a potential compromise and disables a privileged account.
The agent may have correctly identified suspicious behavior.
But what if the administrator was performing an authorized emergency change?
What began as an automated security response could suddenly become a production outage.
The problem isn't necessarily the AI's ability to analyze information. It's the authority we've given it to act without sufficient context.
Just because AI can make a decision doesn't mean it should automatically have permission to execute it.
Who Is Steering the AI SOC?
This is where I believe the conversation around AI security needs to evolve.
The industry is increasingly focused on how much work AI agents can automate. I'm equally interested in who defines their boundaries, validates their decisions, and remains accountable for the results.
In our canoe, I didn't need the steersperson to explain every adjustment. I needed confidence that someone understood where we were going.
An AI-powered SOC shouldn't require human approval for every routine investigation or alert classification. That would undermine much of the value AI delivers.
However, consequential actions, such as disabling privileged identities, isolating critical infrastructure, or modifying security policies, require stronger safeguards.
I believe the most practical approach is a hybrid security model:
AI provides speed, scale, investigation, and execution within authorized boundaries. Humans establish the mission, define acceptable risk, and retain accountability.
The objective isn't to slow AI down. It's to ensure greater autonomy doesn't come at the expense of security or operational control.
But Who Protects the Agents Protecting Us?
There is another dimension to this conversation.
What happens when the AI security agent itself becomes the target?
Security agents consume information from endpoint telemetry, emails, service tickets, threat intelligence feeds, and other systems.
Some of that information could be manipulated by an attacker.
Through prompt injection, compromised integrations, or malicious data sources, attackers may attempt to influence an agent's reasoning or redirect its actions.
An agent with excessive privileges could unintentionally become a pathway to unauthorized system changes or sensitive data exposure.
This is why Zero Trust principles must extend beyond users, devices, and applications to include AI agents themselves.
Every agent needs a defined identity, limited permissions, clear responsibilities, and independently enforced authorization controls.
Trust should never be assumed simply because an agent belongs to the security team.
Observability: Understanding Every Decision
In paddling, coordination requires timing, awareness, communication, and the ability to respond when conditions change.
In an AI SOC, observability plays a similarly important role.
Organizations must understand not only what's happening across their infrastructure, but also how their AI agents are behaving.
What information did an agent access? Which tools did it use? What evidence influenced its recommendation? Did it operate within its permissions?
And perhaps most importantly, can we identify, stop, or reverse an incorrect action?
These questions become increasingly important when multiple agents exchange information and act on one another's conclusions.
Frameworks such as NIST CSF and ISO/IEC 42001 provide useful foundations for governance and accountability. But effective security also requires technical enforcement through identity controls, monitoring, policy-based authorization, and independent validation.
Policies establish expectations. Technical guardrails enforce them.
The Future SOC Isn't About Replacing the Crew
I don't believe the success of an AI SOC should be measured primarily by how many analysts it replaces.
It should be measured by better security outcomes.
Faster investigations. Fewer false positives. Earlier threat detection. More consistent responses. Less operational disruption.
As organizations gain confidence in these systems, AI agents can progressively earn greater autonomy through demonstrated accuracy, reliability, and transparency.
The goal isn't autonomy for its own sake.
It's building a more capable security operation where humans and AI work together effectively.
Back to the Fourth Seat
When I look back at this photograph from the 2023 HCRA State Championship, I see more than a canoe race.
I see individuals with different responsibilities working toward one objective, where trust, discipline, and coordination matter as much as individual strength.
From the fourth seat, I didn't need to control everything happening around me. I needed to understand my role, remain synchronized, and trust the structure that allowed our crew to perform.
I believe organizations adopting Agentic AI can learn something from that experience.
At Emmasanti.ai, we approach AI adoption as an organizational transformation involving people, processes, technology, governance, and trust.
The AI SOC is a compelling example of that transformation.
As AI becomes more capable of independently investigating threats, collaborating with other agents, and executing actions, we must become equally sophisticated in how we establish boundaries and accountability.
Because whether we're racing across the ocean or defending an enterprise, success isn't determined solely by how fast or how hard we move.
It's determined by how well we work together, the trust we establish, and whether we're all moving in the right direction.
Sometimes, an important lesson about the future of AI comes from a seat in an outrigger canoe.